Inside The Banzai IoT Hack: What Tomtchblog Revealed And How To Protect Your Devices (2026 Analysis)
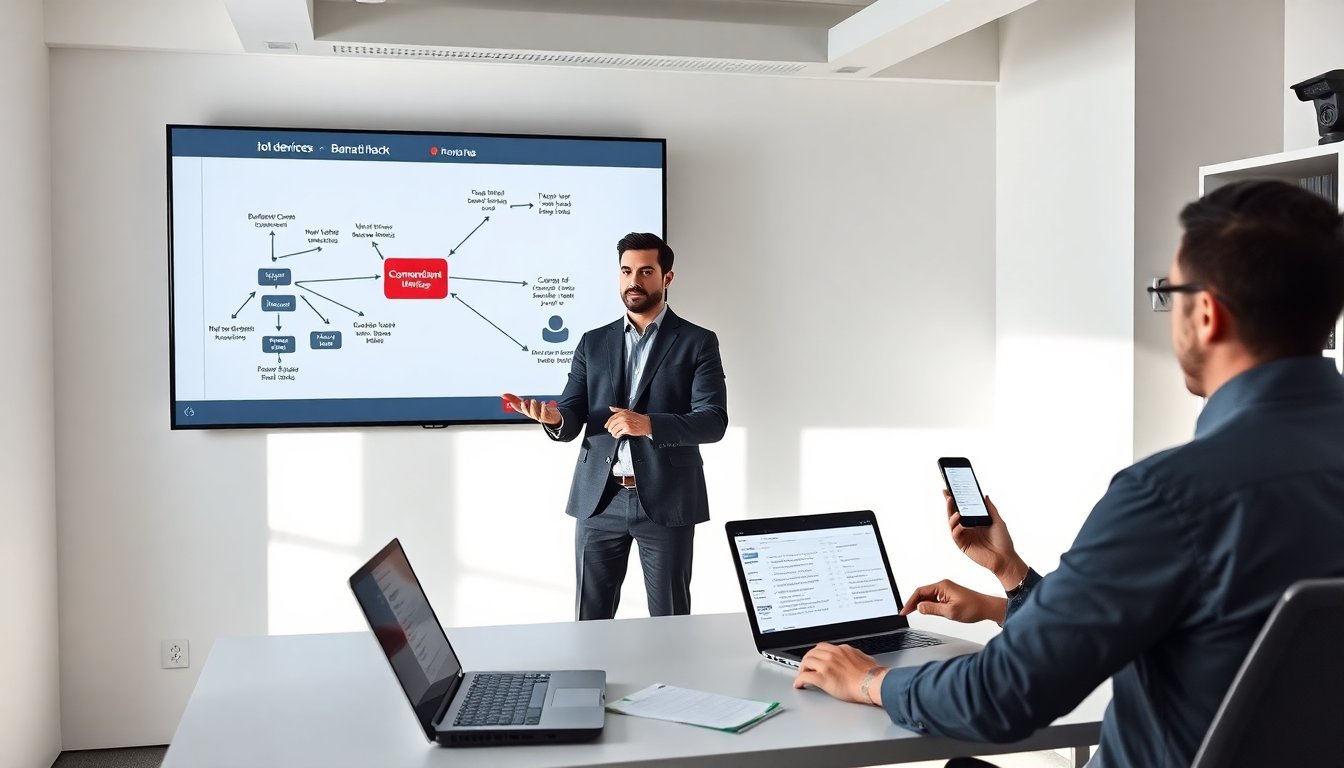
Tomtchblog published a detailed report on the iot devices banzai hack that affected many home and business devices. The report showed how attackers gained access and moved laterally. The article summarizes Tomtchblog’s findings and gives clear actions to reduce risk. Readers will learn what happened, which devices face risk, and simple steps they can take now to secure devices and networks.
Key Takeaways
- The IoT devices Banzai hack exploited exposed management interfaces with default credentials, enabling attackers to gain control rapidly.
- Devices such as routers, IP cameras, NAS units, and smart plugs running default settings were most at risk in the Banzai exploit.
- Indicators of compromise include new user accounts, unusual outbound connections on uncommon ports, and processes mimicking system binaries, which should be actively monitored.
- Immediate security steps include changing default passwords, disabling unused services like Telnet, segmenting IoT from sensitive networks, and applying all firmware updates.
- Blocking outbound traffic to known command-and-control domains and enabling centralized logging can help detect and prevent further Banzai hack activity.
Attack Vector And Technical Breakdown Of The Banzai Exploit
Tomtchblog outlined the initial entry point for the iot devices banzai hack as exposed management interfaces. The researcher showed how an automated scanner found Telnet and HTTP endpoints. The attacker used default usernames and passwords to log in. The exploit then uploaded a compact shell script that fetched additional binaries. The binaries contained a loader, a scanner, and a controller module. Tomtchblog provided hashes and sample network indicators for detection. The analysis stressed that weak device configuration enabled the exploit to succeed.
Timeline Of The Breach And Key Indicators Of Compromise
Tomtchblog reconstructed a concise timeline for the iot devices banzai hack. The scanner activity began on a weekend and peaked within hours. The initial login occurred within minutes of discovery. The loader executed and called out to a command server within an hour. The malware opened persistent reverse shells and added scheduled tasks. Key indicators included new user accounts, unusual outbound connections on uncommon ports, and unexpected processes named like common system binaries. Tomtchblog advised monitoring for those signs and sharing IOCs with security tools.
Who And What Were Affected: Devices, Networks, And Data Risks
Tomtchblog showed that routers, IP cameras, NAS units, and smart plugs were common victims in the iot devices banzai hack. Many devices ran default admin accounts or had open Telnet. Small business gateways that linked IoT devices to corporate networks also suffered. The attackers used infected IoT hosts to scan internal ranges and to relay traffic. Tomtchblog warned that the campaign increased risk to internal servers and to data on network shares. The report noted that attackers could add the devices to a botnet, conduct DDoS, or stage further attacks from those hosts.
Immediate Steps To Secure At-Risk IoT Devices Right Now
Tomtchblog recommended immediate actions to halt the iot devices banzai hack. They advised segmenting IoT networks from business or sensitive networks. They advised changing default passwords to strong, unique ones. They advised disabling unused services, especially Telnet and remote management. They advised applying firmware updates and rebooting devices after patching. They advised checking firewall rules and blocking outbound connections to known C2 domains listed in the report. They advised enabling logging and forwarding logs to a central collector for analysis.
Author